


Integrate Quickly
Connect existing applications and workflows without building a private AI infrastructure stack from scratch.
Your application shouldn't have to send sensitive data to a public AI service just to use a powerful model. Enclave AI provides private AI inference through an enterprise-ready API.
The API Private Layer
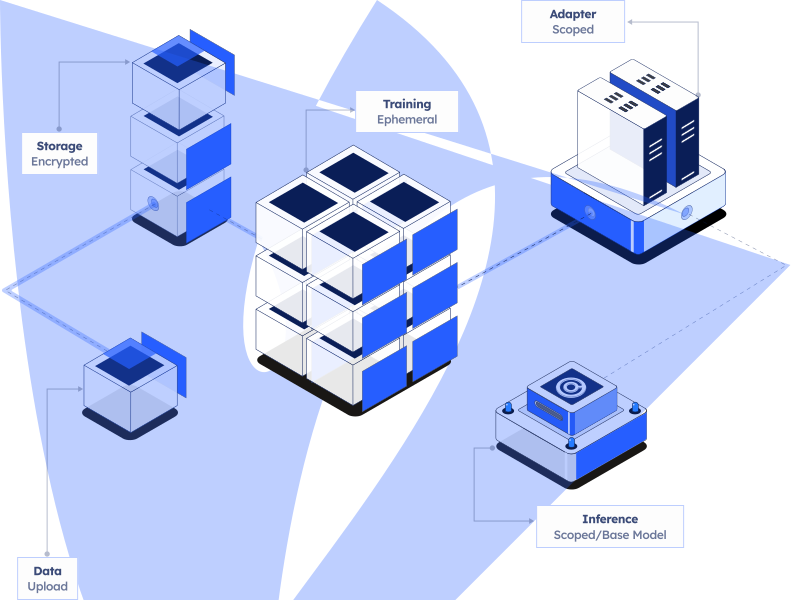
Enclave AI gives developers a simple way to integrate powerful AI while keeping sensitive workloads inside controlled, isolated infrastructure. Build the application you want. Let Enclave AI handle the private inference environment behind it.
Run sensitive AI workloads inside controlled environments rather than relying exclusively on public AI endpoints.
Connect applications and workflows through an API-based interface designed to fit into modern development stacks.
Connect applications and workflows through an API-based interface designed to fit into modern development stacks.
How It Works
The workflow is deliberately simple: connect, protect, process, return, and govern.
Integration
Keep your application architecture flexible while moving the AI execution layer into a managed private environment.
Connect existing applications and workflows without building a private AI infrastructure stack from scratch.
Access supported models for reasoning, generation, extraction, classification, summarization, and other AI workloads.
Keep your application separate from the underlying model and infrastructure layer so your AI stack can evolve.
Start with the capacity you need and move toward dedicated infrastructure as inference requirements grow.
Protect sensitive prompts and outputs throughout the inference lifecycle with confidential computing.
Apply the operational visibility and deployment controls enterprise AI teams need as usage grows.
Public AI vs Enclave AI
The API call may look similar. The security boundary does not have to be.
Security
Your application already has security controls. Your network has security controls. Your databases have security controls. The AI inference layer should have them too.
Regulated Industries
EncAI is designed for organizations where the value of AI is high - and the cost of exposing sensitive information is even higher.
Healthcare
Support clinical documentation, medical knowledge, internal assistants, administration, analytics, research, and other sensitive healthcare workflows.
Legal
Power document analysis, contract intelligence, legal research, matter workflows, knowledge management, and more.
Finance
Apply private inference to research, risk, compliance, document intelligence, internal knowledge, and financial workflows.
Models
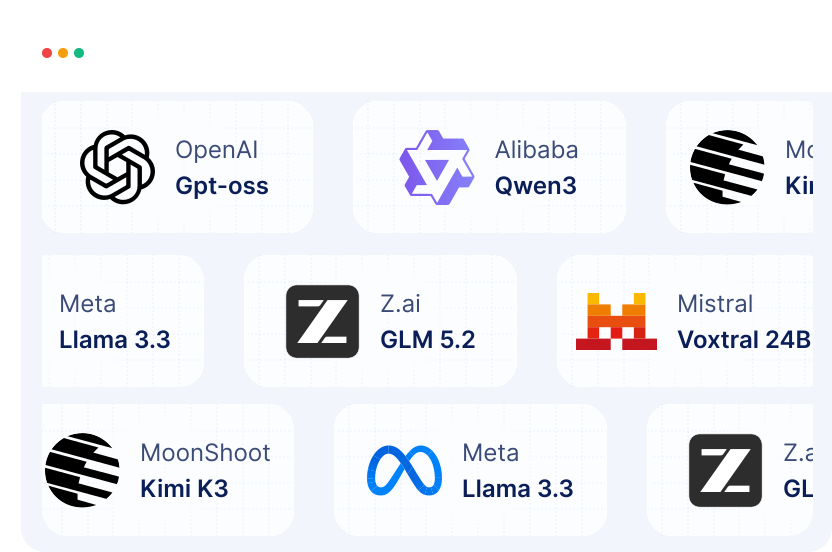
AI is evolving quickly. Your architecture should remain flexible enough to use the right model for the right workload.
OpenAI-compatible LLM endpoints with private prompts and verifiable runtime states - enabling secure deployment of your own custom Docker workloads.
Enterprise Governance
The AI layer needs to fit into the organization's broader security and governance model, especially when applications handle regulated or confidential data.
Compliance
Requirements for information security management, data protection, privacy, and responsible handling of sensitive information.
Request for DocumentationCompliance
Designed to support HIPAA requirements for safeguarding sensitive patient information and maintaining healthcare data privacy.
Request for DocumentationCompliance
GDPR-ready requirements for data protection, privacy, and responsible handling of personal information.
Request for DocumentationContact Us
Join the waitlist for availability updates, rollout notes, and early cohort announcements.


